


Request sent!
Thanks for reaching out - we've got your details. Someone from the Emphere team will reach out shortly.
Typical response:
within one business day
Done
Done
Oops! Something went wrong while submitting the form.





Build anything,
we keep it patched.
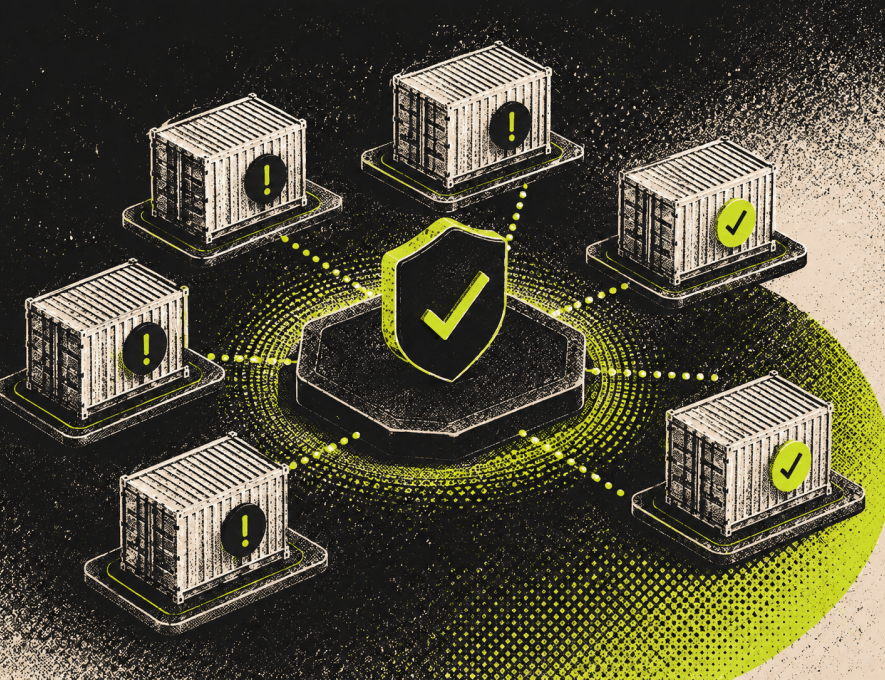
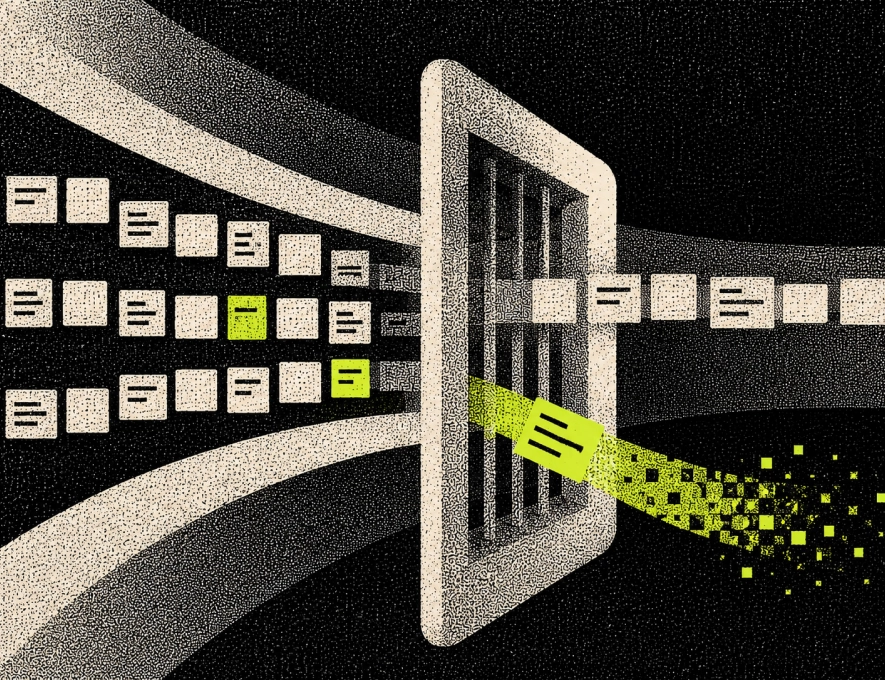
Send Emphere a Dockerfile from a customer-facing product or a representative stand-in. Emphere will return a remediated build with scanner-ready evidence in days.


Sign up for our newsletter to stay in touch.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
By subscribing you agree to Terms of Use, our Privacy Policy and our information collection notice
© 2026 Emphere, All rights reserved.
Emphere provides automated container remediation and verification based on the Dockerfiles and software components supplied by each customer. Security outcomes may vary depending on application configuration, third-party dependencies, scanner coverage, and newly disclosed vulnerabilities.